Customer trust depends on every digital interaction feeling safe, simple, and dependable. Reliable authentication protects accounts, data, payments, and private communications from unauthorized access. It also proves that a business respects each customer relationship. The NIST Digital Identity Guidelines offer useful standards for building stronger identity processes.
Why Customer Trust Depends on Authentication
A customer shares personal information with an organization because they expect responsible protection. Login failures, account takeovers, and confusing recovery steps can weaken that confidence quickly. Reliable authentication creates a consistent security experience across websites, applications, and support channels.
Strong identity controls show customers that security is not an afterthought. They also reduce the likelihood of costly breaches and public reputation damage. Businesses should treat authentication as a vital customer service function.
Reliable authentication supports trust by providing:
- Secure access to customer portals and digital services.
- Better protection for personal and financial information.
- Fewer fraudulent account changes and unauthorized purchases.
- Clear verification during sensitive support requests.
- Faster recovery after suspicious login activity.
Organizations can strengthen this foundation by combining identity protection with resilient data practices. Learn why multifactor authentication and cloud backups improve data security.
Reliable Authentication Protects Every Customer Interaction
Authentication is the process of confirming that someone is who they claim to be. Passwords remain common, but passwords alone no longer provide enough protection. Criminals can steal passwords through phishing, credential stuffing, malware, or data breaches.
Reliable authentication uses multiple signals before granting access. These signals can include something a customer knows, owns, or is. A password is something known. A security key or phone is something owned. A fingerprint is something the customer is.
A layered approach may include:
- Unique passwords stored in a trusted password manager.
- Multifactor authentication for every important account.
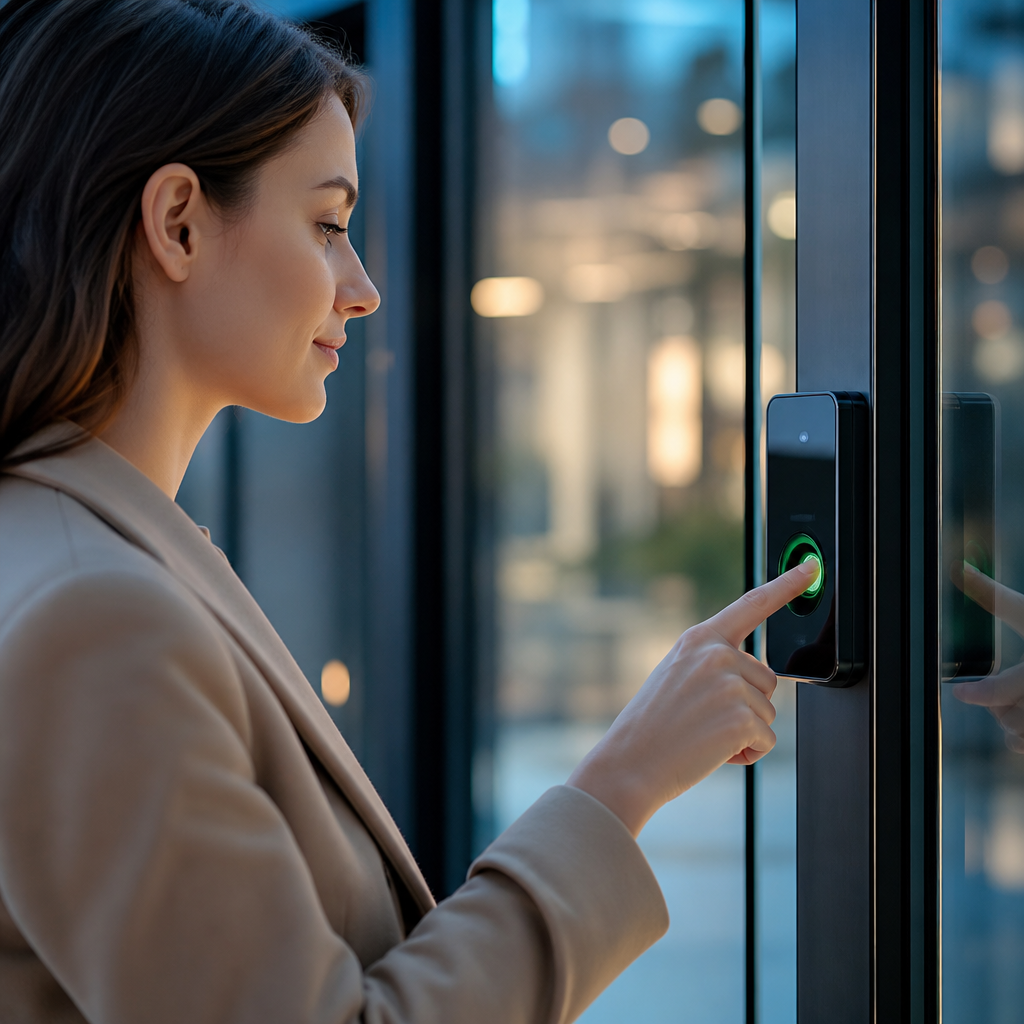
- Biometric verification on supported customer devices.
- Risk-based checks for unusual locations or login behavior.
- Secure account recovery procedures with identity verification.
Multifactor authentication is especially effective because stolen passwords become less valuable. The Cybersecurity and Infrastructure Security Agency MFA guidance explains why this additional layer matters.
Common Threats That Damage Customer Confidence
Cybercriminals often target the easiest path into an account. Phishing emails can imitate trusted brands and direct customers toward fake login pages. Credential stuffing attacks use stolen passwords from unrelated breaches. Social engineering attacks may also manipulate employees into changing customer account details.
One successful incident can affect thousands of customers. It can also create support backlogs, financial losses, and regulatory concerns. Reliable authentication reduces exposure by making stolen credentials harder to use.
Businesses should monitor these warning signs:
- Repeated failed login attempts from one internet address.
- Login attempts from unfamiliar countries or devices.
- Sudden password reset requests after a phishing campaign.
- Multiple customer accounts using compromised credentials.
- Unexpected changes to payment or contact information.
Phishing prevention should support every authentication strategy. Review how smarter phishing protection keeps businesses running for practical risk reduction ideas.
Designing an Authentication Experience Customers Will Use
Security controls only work when customers can complete them confidently. Overly complex login requirements can cause abandonment and unnecessary support calls. A reliable process should balance strong protection with a smooth customer experience.
Start with clear, direct language during registration and sign-in. Explain why an additional verification step protects the customer account. Offer accessible options for people who cannot use certain devices or biometric features.
An effective customer authentication experience includes:
- Short instructions written in plain language.
- Clear error messages that avoid revealing sensitive details.
- Multiple secure verification options when possible.
- Recovery paths that resist identity fraud.
- Consistent login designs across websites and mobile applications.
Password policies should also be practical. Long passphrases often provide better security than complicated short passwords. Businesses should avoid forcing frequent password changes without evidence of compromise.
The OWASP Authentication Cheat Sheet provides technical guidance for secure and usable authentication design.
Build Reliable Authentication Into Daily Operations
Reliable authentication requires more than a login page. It needs ongoing oversight, employee training, tested recovery processes, and secure technology management. Every department handling customer data should understand its responsibility.
Customer support teams need procedures for verifying callers before discussing account details. Marketing teams should protect customer platforms with appropriate permissions. IT teams should review access regularly and remove inactive accounts.
Create a practical authentication program with these steps:
- Require multifactor authentication for administrators and remote workers.
- Apply least-privilege access to customer databases and applications.
- Review access permissions after role changes or departures.
- Monitor authentication logs for suspicious patterns.
- Test account recovery workflows before an emergency occurs.
- Train employees to recognize social engineering attempts.
Authentication controls work best alongside secure backups. Backups help restore operations if ransomware or account compromise disrupts systems. Explore how MFA and data backups stop ransomware attacks before an incident threatens customer service.
Measure Results and Improve Customer Security
Security is not a one-time project. Threats evolve, customer expectations change, and technology platforms receive updates. Regular measurement helps organizations identify weak points before criminals exploit them.
Track both security outcomes and customer experience. A low fraud rate matters, but so does a low rate of unnecessary login failures. Review feedback from customers who struggle with verification or account recovery.
Useful metrics include:
- Multifactor authentication enrollment rates.
- Failed login and account lockout trends.
- Time required to resolve account recovery requests.
- Confirmed account takeover incidents.
- Customer support requests related to login problems.
- Employee response times for suspicious authentication alerts.
Review these metrics monthly or quarterly. Use the results to improve instructions, security settings, and internal processes. Independent assessments can also reveal overlooked weaknesses.
For local organizations, reliable managed IT support in New Philadelphia can help align security controls with operational needs.
Final Thoughts
Customer trust grows when every login feels secure, clear, and dependable. Reliable authentication protects valuable relationships while reducing fraud, disruption, and reputational risk. Invest in layered identity controls now, and give every customer a stronger reason to trust your business.