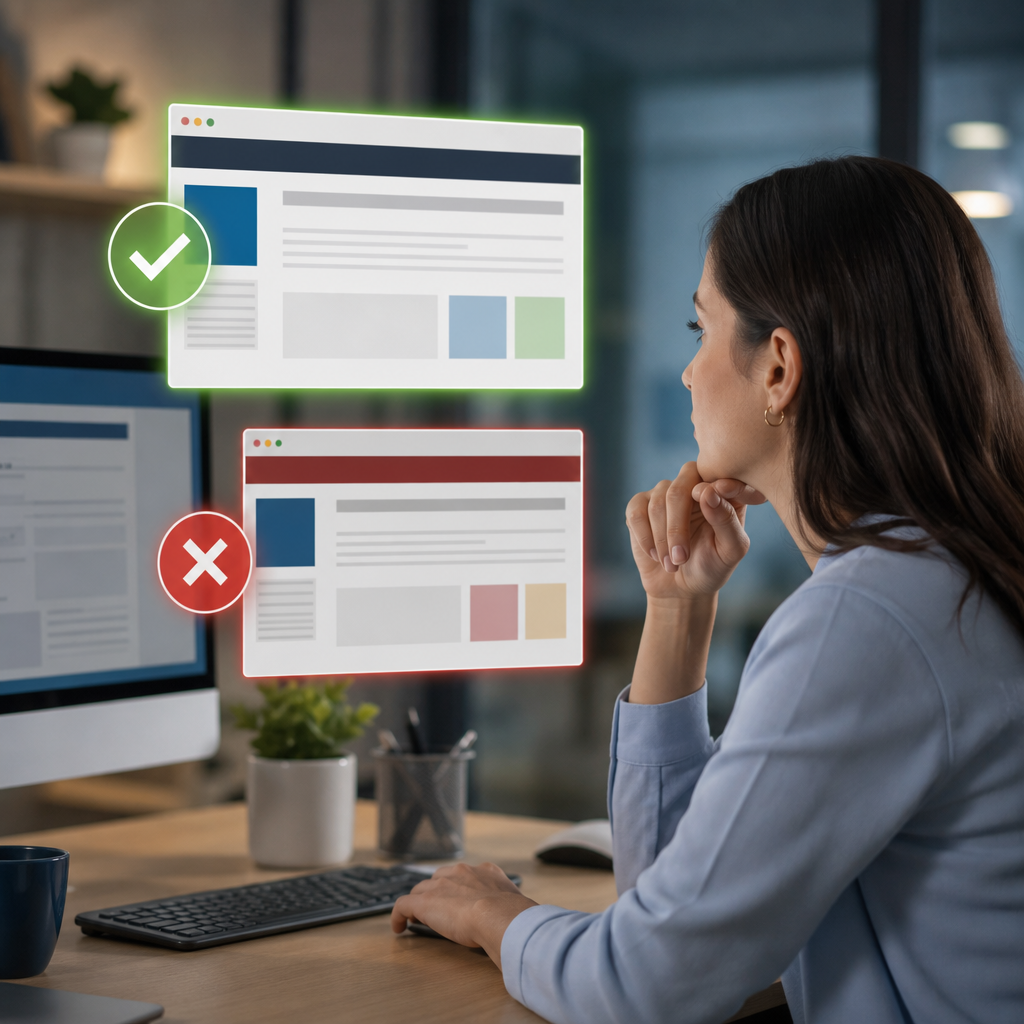
Phishing attacks often succeed because fraudulent messages imitate familiar tools. A reliable page shell gives employees a consistent visual reference point. It makes unexpected layouts, login screens, and navigation patterns easier to question. Combined with cybersecurity awareness training, familiar design standards can reduce costly security mistakes.
What Is a Page Shell?
A page shell is the consistent outer framework of an application or website. It usually includes logos, navigation, headers, footers, colors, and account controls. Employees learn these details through regular use.
A reliable page shell does not guarantee that a page is safe. However, it helps employees recognize when a screen looks unfamiliar. Criminals frequently copy branding but overlook subtle structural details.
The CISA phishing guidance recommends verifying suspicious requests before sharing information. Consistent page design supports that verification process.
Common page shell elements include:
- A recognizable company logo placed in the expected location.
- Consistent navigation menus and department links.
- Standard colors, fonts, and button styles.
- Known account menus and profile controls.
- Clear privacy, support, and contact links.
- Approved domain names displayed in the browser address bar.
Why Consistency Helps Employees Spot Phishing
Employees make quick decisions during busy workdays. Attackers exploit urgency, familiarity, and routine behavior. A reliable page shell creates visual patterns that employees can remember.
For example, a fake payroll portal may copy a company logo. Yet, it may lack normal navigation or use unusual spacing. It might also display a generic support link. These differences can signal phishing before credentials are entered.
The National Institute of Standards and Technology stresses risk-based cybersecurity practices. Visual consistency supports this approach by making risky pages easier to identify.
Employees should pause when they notice:
- Missing navigation links that normally appear on internal portals.
- Logos that look blurry, stretched, or incorrectly positioned.
- Different button colors or unusual form field labels.
- Login pages requesting unexpected personal information.
- Broken links, spelling errors, or inconsistent company language.
- Browser addresses that differ from approved company domains.
The Reliable Page Shell and User Trust
Trust is necessary for productive digital work. Employees need confidence when accessing email, payroll, benefits, customer platforms, and internal resources. Still, trust should be informed rather than automatic.
A reliable page shell gives users an expected experience across approved systems. When a page breaks that experience, employees have a reason to stop. They can verify the request through another trusted channel.
Phishing pages often create pressure with messages about account suspension or urgent payments. A familiar design framework helps employees focus on details instead of reacting emotionally. This approach complements proactive cybersecurity awareness training.
A trustworthy employee experience should include:
- Clear guidance about approved business applications.
- Easy access to IT support contacts.
- Standardized login workflows across business systems.
- Notifications that explain why information is requested.
- Visible reporting options for suspicious emails or pages.
- Regular reminders about verified company domains.
Design Signals That Phishing Pages Often Miss
Attackers can clone individual elements quickly. Reproducing a complete, reliable page shell is harder. Legitimate applications contain many interconnected visual and functional signals.
A phishing page may mimic a sign-in form successfully. However, it may not recreate page behavior correctly. Footer links may fail. Account menus may not work. Navigation could lead nowhere.
Employees should review more than the logo. They should consider the full page experience. The Federal Trade Commission phishing resource explains why verification matters before responding to requests.
Useful page shell checks include:
- Does the page use the usual company navigation structure?
- Does the browser address match the known company domain?
- Do support, privacy, and policy links work correctly?
- Is the page asking for information outside normal procedures?
- Does the login process match the usual multi-factor authentication flow?
- Did the page open from an unexpected email or text message?
Pair Page Shell Standards With Multi-Factor Authentication
A reliable page shell improves visual recognition, but it cannot stop every phishing attempt. Attackers may use legitimate-looking pages and stolen domains. Organizations need layered protection.
Multi-factor authentication helps protect accounts when passwords are exposed. Endpoint protection can also detect malicious files or suspicious activity. These tools provide defenses beyond employee observation.
Learn more about multi-factor authentication and endpoint protection for business performance. Strong identity controls reduce the damage caused by compromised credentials.
Businesses should combine page shell standards with:
- Phishing-resistant multi-factor authentication methods.
- Email filtering and domain protection tools.
- Endpoint detection and response capabilities.
- Secure password management policies.
- Fast incident reporting procedures.
- Regular vulnerability and access reviews.
Train Employees to Verify, Not Guess
Employees should never feel embarrassed about reporting suspicious content. Reporting creates valuable security intelligence. It also gives IT teams opportunities to block dangerous domains.
Training should use realistic examples of genuine and fraudulent pages. Show employees the normal page shell for key company systems. Then, explain the warning signs that indicate phishing.
Training works best when it is ongoing. Attackers adapt their messages, branding, and tactics. Short, repeated lessons help employees retain practical habits.
The CISA training resources can support internal phishing education. Businesses can also create tailored examples based on their own applications.
Effective employee training topics include:
- How to inspect browser addresses before entering credentials.
- How to identify unexpected login prompts.
- How to use bookmarks for essential business portals.
- How to report suspicious messages quickly.
- How to verify requests through known phone numbers.
- How to recognize urgent language as a manipulation tactic.
Create a Stronger Page Shell Governance Process
Consistency requires ownership. Marketing, IT, human resources, and application teams should align on approved design elements. This process reduces confusion across employee-facing systems.
Maintain a simple inventory of authorized domains and business applications. Make the list easy for employees to find. Update it whenever a vendor, portal, or login process changes.
Reliable design also supports incident response. If employees know what normal pages look like, they can provide better reports. IT teams can investigate suspicious pages faster.
Organizations should consider these governance practices:
- Document approved logos, colors, and navigation patterns.
- Publish official links through a protected employee portal.
- Review vendor login pages before deployment.
- Notify employees before major portal design changes.
- Test phishing reporting workflows regularly.
- Keep reliable backups for recovery after security incidents.
For broader resilience planning, review smart data backup solutions for modern businesses. Backups help organizations recover if phishing leads to ransomware or data loss.
Key Takeaways
A reliable page shell gives employees a practical visual baseline for spotting phishing attempts. Consistent navigation, domains, branding, and login flows make suspicious deviations more visible.
Design standards must work alongside training, multi-factor authentication, endpoint security, and backups. When employees know what trusted systems look like, they can pause, verify, and report threats confidently.
Leave a Reply
You must be logged in to post a comment.